|
|
By Jeff Poissant, RGD.
Copyright 2026.
|
|
|
|
|
|
|
|
|
|
|
A Digital War Is Upon Us
|
Nefarious actors are no longer limited to manual hunting. They are using AI tools to systematically search for and exploit code errors in the foundational software that runs the global Internet and server applications. In late October 2026, that reality became impossible to ignore.
|
Critical Vulnerabilities in PHP
Researchers (with significant help from frontier AI models) uncovered two critical vulnerabilities in PHP itself — tracked as CVE-2026-109618 and CVE-2026-109619 and widely nicknamed PHP2Shell. Both score 9.2 on the CVSS v4 scale and allow unauthenticated remote code execution. In plain language: an attacker who has never logged into your site can potentially run code on the server.
|
|
These flaws affect virtually every PHP installation that serves web requests (WordPress, Shopify, WIX, Square, custom applications, many control panels, and more). The vulnerable code paths date back more than a decade. Attack attempts were observed before the official patches even existed.
|
This is exactly the scenario I talk about regularly: a security plan to protect critical company information is no longer optional. It is operational hygiene.
|
|
|
|
|
|
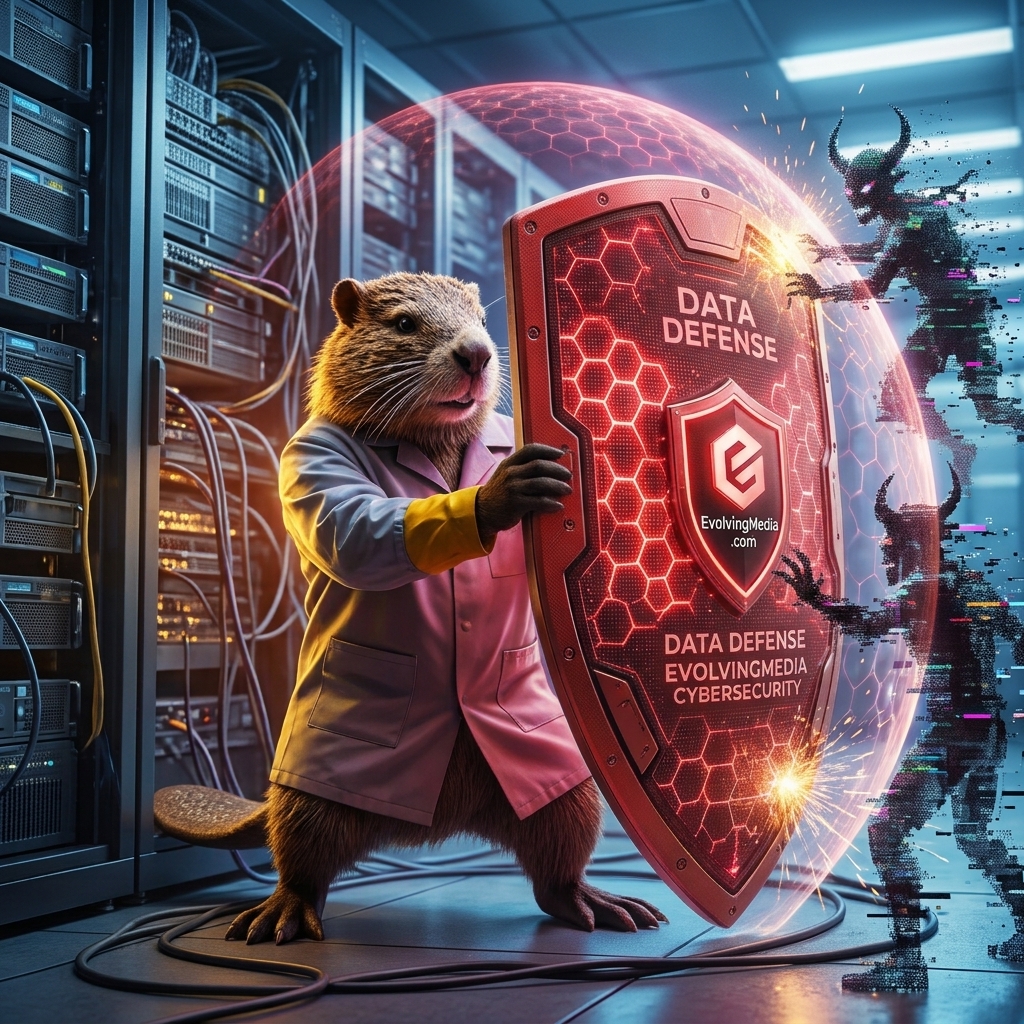
At Evolving Media & Design, I treat infrastructure security as a core responsibility, not an afterthought. When the emergency PHP releases dropped on 21 October 2026 (versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35), I moved quickly:
|
- Identified every managed environment running PHP
- Applied the official security releases
- Restarted PHP workers and verified the new versions were live
- Confirmed no residual exposure on client sites under our care
|
The result was clean, efficient patching with minimal disruption. That is the practical difference between having a plan and hoping for the best.
|
|
|
Why This Matters Beyond One Vulnerability
|
PHP powers a huge portion of the web. When a flaw lives in the language runtime itself, application-level security (plugins, themes, firewalls) cannot fully protect you. The only complete fix is updating the underlying PHP version and restarting the workers.
|
Partial mitigations exist, but the PHP project was explicit:
|
|
|
|
“There are no complete mitigations; updating is the only safe choice.”
|
|
|
AI is accelerating both discovery and exploitation. Researchers used advanced models to find and prove these issues faster than traditional methods alone. Attackers are already doing the same. The window between disclosure and weaponization is shrinking.
|
|
Several cybersecurity and threat intelligence firms have published data highlighting the widespread global impact of the PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619):
|
Global Organization Impact:
According to telemetry from Check Point Research, approximately 10% of organizations worldwide were impacted by exploitation attempts following the early leak of details.
Geographic Concentration:
Security researchers noted that Europe bore the brunt of the initial attack waves. The scale of the threat prompted precautionary measures overseas, including government institutions in countries like the Netherlands and Finland temporarily taking select websites offline.
Web Footprint Estimation:
|
Because PHP is embedded in the foundation of server-side web frameworks, industry estimates indicate that the underlying vulnerabilities affected a vast majority—nearly 70%—of web applications and sites globally prior to patching.
|
Attack Timing:
Telemetry from Cloudflare and other monitoring networks detected early, automated scanning and exploitation attempts starting at 07:43 UTC on October 21, 2026—several hours before the official upstream patches and detailed security advisories were publicly released at 14:00 UTC.
|
|
A digital war is already underway. The weapons are automated, the targets are foundational, and the cost of delay is high.
|
When a critical flaw sits in a foundational language runtime rather than a high-level plugin, automated scanning hits globally within hours, making rapid patch deployment essential.
|
If you manage websites, applications, or client data, ask yourself:
|
- Do you know exactly which PHP versions are running in production?
- Can you apply critical patches within hours, not days?
- Is there a documented process for verification and rollback?
|
If the answer to any of those is unclear, it is time to put a real security plan in place.
|
|
|
|
|
|
|
|
The Garry Fen - Growth Package
Growing businesses wanting page-builder flexibility and room to scale.
|
|
✓ Canadian Managed VPS Infrastructure with Free Basic Domain-Level SSL Certificate
|
|
✓ Pre-installed WordPress + Breakdance Pro Included
|
✓ Generous Data Transfer / Bandwidth with 15 Professional Email Accounts
|
$26.99/Month
Billed annually at $323.98
|
|
|
|
|
A different approach is taken here. Upon selecting your web hosting plan, you'll be asked to create a new account in our Client Care Portal, choose the desired package and payment duration (monthly or annually), and pay for your order by credit card or by Interac e-transfer. Once payment is received, I'll call you to help set up your selected hosting plan and email addresses.
|
|
|
|
For readers who want the primary sources:
|
- PHP Project security advisory (21 October 2026): official description of CVE-2026-109618 and CVE-2026-109619, affected versions, and the “update now” guidance.
- InfoQ and multiple security research firms (including reports from Amazon Threat Intelligence, Cloudflare, Wiz, and others) documented early exploitation attempts and the role of AI in discovery.
- CISA and national CERTs issued urgent guidance to patch or isolate exposed systems.
|
I help Eastern Ontario businesses (and beyond) keep their digital foundations solid — hosting, maintenance, proactive monitoring, and rapid response when the next critical issue appears. If you would like a quiet conversation about your current posture, just reply to this email.
|
|
|
|
About Evolving Media & Design Inc.
A Canadian company
Here are our key services, core disciplines that enable Jeff Poissant, RGD at Evolving Media & Design Inc, with more than 30 years in the creative space, working with entrepreneurs, businesses, government and organizations of all sizes to create, develop, and promote products and services to a local or international clientele.
|
|
Evolving Media & Design Inc. is an investment. Anchored in tradition, evolving in the present, looking forward to the future.
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
|
Evolving Media & Design Inc.
|
57 Gauthier St, Alexandria, ON, K0C 1A0
|
|
All Rights Reserved. Copyright 2026
|
|
  
|
|
|
|
|
|
|
About the Author:
Jeff Poissant, Founder of Evolving Media & Design Inc.
Jeff Poissant, RGD, is the founder and Creative Media Specialist behind Evolving Media & Design Inc., based in eastern Ontario. With over 30 years of hands-on expertise in graphic design, photography, videography, and web development, Jeff crafts multidisciplinary solutions that blend artistry with strategy—delivering captivating visuals and seamless digital experiences to elevate brands in today's dynamic landscape. As the driving force behind our e-newsletter, Evolving Media Chronicles, he shares insights drawn from decades of innovation to empower your creative journey. Ready to transform your vision into reality?
|
|
|
|
|
|
|
|